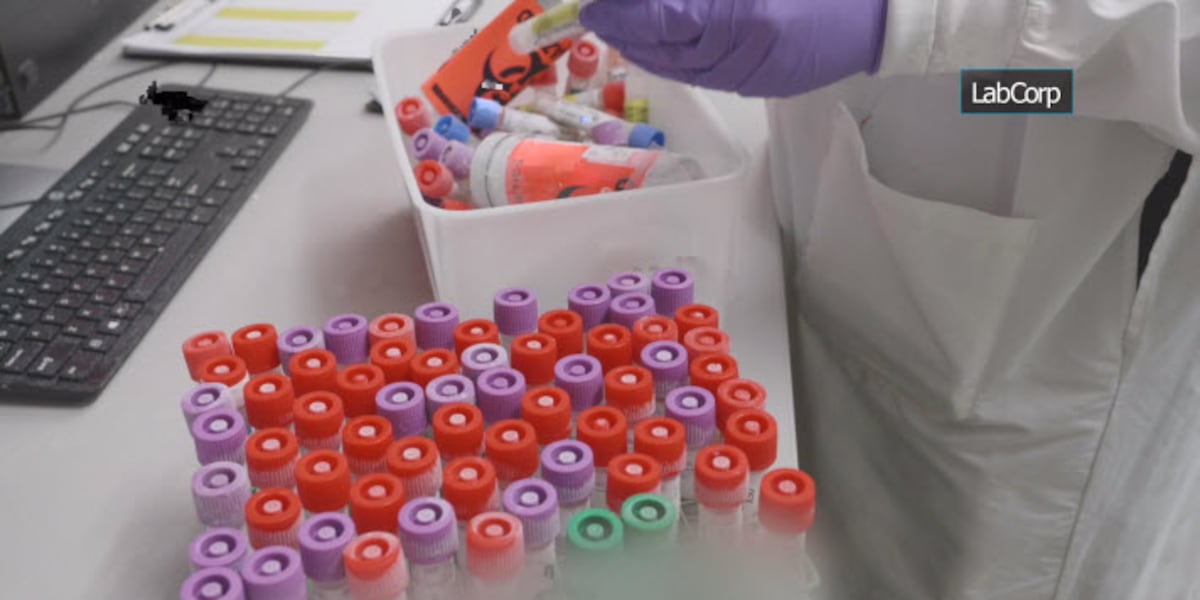

LAS VEGAS (FOX5) — Nevada has joined a 44-state coalition in reaching a $2.3 million settlement with Laboratory Corporation of America following an investigation into a major patient data breach, Attorney General Aaron D. Ford announced Thursday.
The agreement resolves a multistate probe into a 2019 cybersecurity incident involving Labcorp’s former medical debt collection vendor, Retrieval-Masters Creditors Bureau, doing business as the American Medical Collection Agency (AMCA).
Under the terms of the settlement, Labcorp will pay $2,287,455 across participating states, with Nevada receiving $31,178. The company has also agreed to a separate $35 million settlement in a related federal class-action lawsuit.
MORE ON FOX5: Rosen amends proposed bill to ban Trump from using tax dollars on self-promoting ads
The AMCA breach exposed the personal and health data of more than 27.5 million Americans, including roughly 10.2 million Labcorp patients. Across Nevada — where Labcorp operates 20 patient service centers, including multiple facilities throughout Las Vegas, Henderson and North Las Vegas — 123,412 consumers had personal information compromised, with 11,805 having their Social Security numbers exposed.
“When Nevadans trust companies with their sensitive medical and personal information, they expect it to be protected,” Ford said in a statement. “Companies cannot outsource that responsibility. This settlement holds Labcorp accountable and requires stronger safeguards to protect patient data.”
State investigators emphasized that while the breach physically occurred on AMCA’s servers, healthcare entities bound by HIPAA retain an obligation to oversee third-party vendors handling protected health data.
As part of the settlement, Labcorp must implement overhauled vendor oversight protocols, particularly for debt collection agencies. Mandated safeguards include:
- Minimizing patient data shared with debt collectors to what is legally required.
- Establishing a dedicated vendor risk management team equipped with continuous compliance auditing tools.
- Contractually mandating third-party cybersecurity audits, data segmentation, and immediate termination clauses for security failures.
- Enhancing corporate incident response procedures to track vendor-related security incidents.
- Engaging an independent third-party assessor to review the company’s information security posture.
The multistate investigation was led by attorneys general from Connecticut, Florida, Indiana, Illinois, Michigan, and Texas, with assistance from an executive committee that included New York, Tennessee, Maryland, and North Carolina.
Copyright 2026 KVVU. All rights reserved.